


Why Your WordPress Site Is Slow and Expensive to Maintain (2026)
November 2, 2026

If you need help turning a Cursor-built app into production software, the kind of help you need depends on one thing: whether anyone has been reading the code Cursor wrote. There are four kinds of help: a firm that audits the app and then takes it over, a solo senior engineer who rescues it, a fixed-price audit shop, and an AI review tool your own developers can add today. This roundup compares six, says which buyer each fits, and gives a price only where the firm publishes one. Razoyo is listed first because this is Razoyo’s blog, so every other entry says where that firm beats us.
| Option | What it is | Best for | Where | Starting price, if published |
|---|---|---|---|---|
| Razoyo | Software engineering firm | A Cursor app real customers will rely on, audited and then run by the same team | The Colony, Texas (Dallas-Fort Worth), US-wide | $2,500 fixed, Production Spec |
| Red Leg Dev | Veteran-owned software studio, one senior engineer | A founder who wants one senior engineer to stabilize the code | Lakeland, Florida, and remote | $1,500 audit; rescues $15,000 to $50,000 |
| TechAhead | AI and product engineering company | A larger company that needs security review and delivery capacity | USA, India and the UAE | Not published |
| SpringCode | Two-engineer audit and fix shop | A small app that needs a fixed quote, fast | Not stated on its site | Security audit from $700; code audit from $800 |
| Tepesoft Systems | Small software studio | A severity-ranked launch check in 48 hours | Not stated on its site | $500 audit; fixes $1,500 to $5,000 |
| Cursor Bugbot | AI code review tool, not a firm | A team with developers who want every pull request reviewed | Software tool | Included from Cursor’s $30 a month Premium plan |
Disclosure: this is Razoyo’s blog, and we are biased.
Razoyo is a software engineering firm in The Colony, Texas (Dallas-Fort Worth), serving clients US-wide since 2011. We take prototypes and constrained systems into production. We build with agentic AI ourselves, with senior engineers in the loop, so we do not start from distrust of AI-written code.
Our AI-generated code audit names Cursor alongside Lovable, Replit, Bolt.new, v0, Bubble and Windsurf, and says plainly that the tool is not the point: the same seven-dimension check applies whichever one built the app. Security and access, data integrity, architecture, test coverage, observability and alerting, a real deploy path, and documented ownership. It is sold as a Production Spec: $2,500 fixed, with audit findings, a risk ranking, a remediation plan and a straight harden-or-rebuild call. Most of what a good prototype captures, the workflow, the intent and the rough data model, is worth keeping, and the audit decides salvage versus rebuild on the evidence.
Spider, the hotel business intelligence platform now part of Lighthouse, is our production proof. It was not AI-built: it was an internal tool that outgrew its first version, and more than 10,000 people a day now use it. Spider ranked #1 of 74 for Business Intelligence at the 2025 HotelTechAwards. We have also delivered systems for several Fortune 500 companies, always under NDA, so we name none of them.
After the Spec, the published price list: an MVP from $5,000, a production build from $10,000, support from $1,500 a month. Before any work above the Spec, a business analyst puts a level of effort and a budget on each piece and gets your confirmation first. No approval, no work.
Ideal for
Why they stand out
Razoyo publishes the seven things it checks, the price of checking them and what happens after. The audit costs the same whether the answer is three fixes or a rebuild, so there is no reason to sell you the bigger job.
Pros
Cons
Verdict: pick Razoyo when the Cursor app will carry real customers and you want one accountable team for the audit, the fixes and the years after.
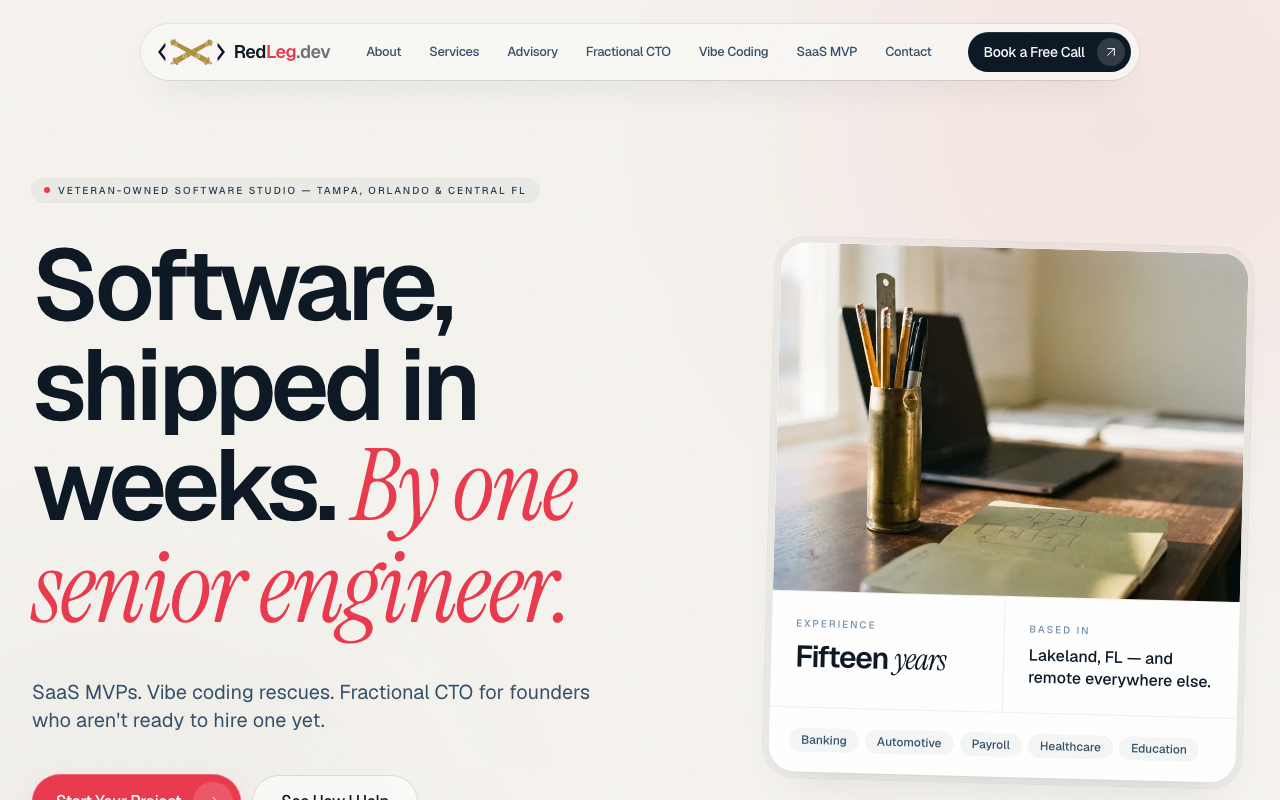
Red Leg Dev is a veteran-owned software studio in Central Florida, based in Lakeland and remote everywhere else. Its founder, Matt Wagner, describes fifteen years of SaaS work, most of it as the one person on the engineering side, and the homepage promises software “by one senior engineer.”
Its Cursor page is the most specific diagnosis we found. It argues that Cursor did not write bad code, nobody reviewed the diffs: agent mode can rewrite dozens of files in one pass, large diffs get accepted under deadline pressure, and different prompts and models leave “three different ways of doing the same thing.” Its rescue reads the full commit and diff history, picks one pattern per concern and refactors toward it, rewrites tests that mock out what they should test, scrubs git history for committed secrets and rotates anything exposed, and pins and audits the dependencies. It also says a rewrite is rare for Cursor projects, because a human already reasoned through the logic.
Prices are published: the audit is a $1,500 flat fee with a two-week turnaround, followed by a written report and a fixed-price quote. Most rescues run $15,000 to $50,000 and take two to six weeks.
Ideal for
Why they stand out
It has a Cursor-specific failure list rather than a generic AI-code one, and publishes both the audit price and the typical rescue range.
Pros
Cons
Verdict: pick Red Leg Dev when the Cursor codebase is sound underneath and you want one senior engineer to make it consistent.
TechAhead describes itself as an AI-first company across the USA, India and the UAE, with 16 years of digital engineering, ISO 42001 certification and partnerships with AWS and OpenAI. It builds AI-native apps and platforms and offers dedicated offshore teams.
It has published a detailed guide to hardening an application built with Cursor. The guide’s position is fair: “Using Cursor to build an application neither qualifies nor disqualifies it for production.” It recommends starting from a data-flow map rather than a blanket request to make the app secure, testing authorization and tenant isolation with direct requests, multiple accounts and negative cases, and reviewing secrets, integrations, deployment settings and failure paths. For an existing Cursor app it describes a scoped assessment first: a data-flow and threat map, validated findings, a ranked remediation plan and a recommendation to harden, extend or restructure, followed by an independent verification pass after any fixes. No price is published.
Ideal for
Why they stand out
Its guide treats a Cursor app as a security and operations question, not an AI question, and includes an independent verification pass after the fixes.
Pros
Cons
Verdict: pick TechAhead when the Cursor app sits inside a larger company that needs security review and a bigger team.
SpringCode is founder-led: two senior engineers with 15+ years in security and production systems, who audit, fix and migrate apps built with Cursor, Lovable, Replit, Bolt and Claude Code. You work directly with the people writing your code, and it promises a fixed quote within 24 hours.
Its Cursor page lists the issues it looks for when auditing Cursor apps, drawn from security research and community forums: agents editing files outside the requested scope, git hooks running on untrusted repositories, and indirect prompt injection through connected tools. It also reviews MCP configurations as part of a Cursor codebase review, which few audit shops mention.
Prices are published: a security audit from $700, a full code audit from $800, bug fixes on a custom quote, and a prepaid retainer at $75 an hour (5 hours for $375, 10 for $750). It offers a free 15-minute call.
Ideal for
Why they stand out
It looks at the development environment as well as the code: MCP servers, git hooks and agent scope, which is where Cursor-specific risk sits.
Pros
Cons
Verdict: pick SpringCode for a small Cursor app that needs a cheap, fast, fixed-price audit.
Tepesoft Systems is a small software studio behind long-running desktop software and focused web products. It says it mostly builds for US businesses while serving clients worldwide, and today sells AI workflow automation alongside production hardening.
Its Production Readiness Audit covers apps built with Lovable, Bolt, Replit, Cursor, v0 or AI-heavy freelancers, before customers see the product. It returns a launch-risk report ranked by severity, reviews auth, database, API, permission and deployment, and ends with a keep, fix, replace or rebuild recommendation, plus an optional rescue sprint for critical issues.
Its pricing page is specific: the AI-Built App Launch Safety Audit is $500, with a 48-hour screen and a 7-day fix plan. Fix sprints run $1,500 to $5,000 over 7 to 14 days, and ongoing stability care is $750 to $2,500 a month.
Ideal for
Why they stand out
It is the fastest and cheapest published audit in this roundup, with the fix price published too.
Pros
Cons
Verdict: pick Tepesoft when you need a severity-ranked launch check this week for the lowest published price.
Bugbot is not a firm. It is Cursor’s own AI code review, which reviews pull requests on GitHub and flags logic bugs before they merge. Cursor says it optimizes for bugs that get fixed, improves as you define custom rules, and quotes customers who say it catches implementation errors that passed human code review.
On Cursor’s pricing page, AI code reviews via Bugbot are included from the Premium plan at $30 a month and on Teams from $30 per user a month. Cursor also supports project rules stored in .cursor/rules, version-controlled with your code, which is how a team stops the agent from inventing a new pattern in every session.
What it does not do: decide whether your architecture holds, test your access model across real accounts, or take responsibility for the app at 2 a.m.
Ideal for
Why they stand out
It reviews the same kind of large AI-authored diff that causes most Cursor problems, at the moment it is proposed.
Pros
Cons
Verdict: pick Bugbot when you have a developer and want every future Cursor change reviewed before it ships.
Mostly because large AI-written changes were accepted without anyone reading every line, not because Cursor writes worse code than other tools. Cursor is a code editor with an agent in it, so a developer is usually in the loop. The risk is process: agent mode can change many files at once, different sessions and models solve the same problem different ways, and the codebase drifts.
The production failures that follow are the ordinary ones, just more frequent:
| Failure | How it shows up | First check |
|---|---|---|
| Broken access control | One user can read another user’s data | Log in as two test users and swap a record ID |
| Secrets in the repository | Keys in the code or the git history | Search the history, then rotate anything found |
| Pattern drift | Three error-handling styles, two HTTP clients | Pick one pattern per concern and write it into project rules |
| Tests that test nothing | Green tests that mock the thing under test | Break the feature on purpose and see if a test fails |
| No deploy or rollback path | A bad release stays live for hours | Time a one-word change out and back |
Access control comes first for a reason. OWASP’s Top 10:2025 keeps broken access control at number one and reports that “100% of the applications tested were found to have some form of broken access control.” On secrets, GitHub’s guidance on removing sensitive data from a repository is clear about order: revoke or rotate the secret first, because rewriting history alone does not make a leaked key safe.
Harden it, usually. Cursor apps are often better candidates for hardening than apps from one-prompt generators, because a person was choosing what to accept. Red Leg Dev says a rewrite is rare for Cursor projects, TechAhead says the tool “neither qualifies nor disqualifies” an app for production, and our own audit page says the workflow and data model a good prototype captures are usually worth keeping.
Rebuild the core when the access model is wrong at the root: one account type that can see everything, customer data with no owner on each record, or a data model that assumes one organization when you now sell to many. Our harden or rebuild page sets out how we make that call, and rewrite or refactor an inherited codebase covers the same decision for code someone else wrote. If the app is already live and falling over, read what to do when an AI-built app stops working first.
You can keep using Cursor. You cannot prompt your way to a decision nobody has made. Cursor will write tests, fix a bug or add a permission check when asked, and it does that well. What it cannot do is decide what your access model should be, notice that three sessions built three error handlers, or tell you that the last release cannot be rolled back. Those are decisions, and someone has to own them.
The practical split: keep building in Cursor, add project rules so the agent follows one pattern per concern, add review on every change (Bugbot, or a human), and have a senior engineer own the architecture and the production checks below. That is how we work ourselves: AI under engineering discipline, with senior engineers in the loop.
Run this before you call anybody, including us. It is the seven dimensions from our AI-generated code audit, each with the test we would run first on a Cursor codebase. Each is pass or fail, and every fail is a line item on the quote you are about to receive.
.cursor/rules.| Result | What it usually means |
|---|---|
| Six or seven passes | Harden it and keep building, with review on every change. |
| Three to five passes | A focused hardening project; an audit sizes it. |
| Security and access fails, with no owner on customer records | Plan on rebuilding the core, keeping the workflow and data model where you can. |
Call the option that matches who owns your code today. Developers in-house who keep building: add Bugbot and project rules. A launch this week and a small budget: Tepesoft or SpringCode. A sound codebase that needs one senior engineer to make it consistent: Red Leg Dev. A larger company with enterprise customers and security questionnaires: TechAhead. A Cursor app real customers will depend on, where you want the audit and the years after from one team: we do that for a fixed $2,500 first, and if the answer is “this needs three fixes, not a rebuild,” that is what you will hear. Every step and price is on our process page, and what it costs to take an AI-built prototype to production breaks the numbers down. If you used Lovable, Replit or Bolt rather than Cursor, the firms that take a vibe-coded app to production covers those tools.
.cursor/rules and version-controlled with the code, which guide the agent’s choices.Who can turn a Cursor-built app into production software? Firms and services that name Cursor on their own sites include Razoyo, Red Leg Dev, TechAhead, SpringCode and Tepesoft Systems. If your own developers will do the work, Cursor’s Bugbot reviews every pull request. Match the option to your app’s size, your budget and whether you want someone to run the app afterward.
Why do apps built with Cursor break in production? Usually because large AI-written changes were accepted without anyone reading every line, and patterns drifted across sessions and models. The failures that follow are ordinary ones: broken access control, secrets in the repository, tests that test nothing and no rollback path.
Should I harden my Cursor app or rebuild it? Usually harden it. Because a person chose what to accept, the logic and data model are often worth keeping. Rebuild the core when the access model is wrong at the root, such as no owner on customer records or a data model built for one organization.
How much does it cost to make a Cursor app production ready? Published prices in this roundup run from a $500 audit at Tepesoft, through audits from $700 and $800 at SpringCode and $1,500 at Red Leg Dev, to Razoyo’s $2,500 fixed Production Spec. Red Leg Dev says most rescues run $15,000 to $50,000.
Can I keep using Cursor after the app is production ready? Yes. Add project rules in .cursor/rules so the agent follows one pattern per concern, review every change with Bugbot or a person, and have a senior engineer own the architecture, the deploy path and monitoring.
What should I check first in a Cursor-built app? Access control and secrets. Log in as two test users and try to open each other’s records. Then search the repository and its history for keys, and rotate anything you find before cleaning the history.
Is Cursor Bugbot enough to make my app production ready? No. Bugbot reviews new pull requests and catches bugs before they merge, which is valuable. It does not audit code already shipped, choose your access model or run the app in production. Someone still has to own those.
If your Cursor app is about to carry real customers and you are not sure whether it needs three fixes or a rebuild, that is a free 30 minute conversation. Run the Seven-Point Cursor Production Check first and bring your results. We will tell you which fails matter, whether a $500 audit elsewhere would answer your question, and what a Production Spec would cover. Schedule Free Consultation. If you do not need us yet, that is what you will hear.
Paul Byrne is President of Razoyo, a software engineering firm in The Colony, Texas taking prototypes and constrained systems into production since 2011.
These links open AI platforms with pre-written prompts about this page.
We use cookies to improve your experience. Do you accept?
To find out more about the types of cookies, as well as who sends them on our website, please visit our cookie policy and privacy policy.
